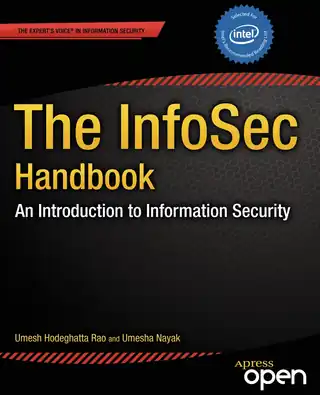
The InfoSec Handbook offers the reader an organized layout of information that is easily read and understood. Allowing beginners to enter the field and understand the key concepts and ideas, while still keeping the experienced readers updated on topics and concepts.
It is intended mainly for beginners to the field of information security, written in a way that makes it easy for them to understand the detailed content of the book. The book offers a practical and simple view of the security practices while still offering somewhat technical and detailed information relating to security. It helps the reader build a strong foundation of information, allowing them to move forward from the book with a larger knowledge base.
Security is a constantly growing concern that everyone must deal with. Whether it’s an average computer user or a highly skilled computer user, they are always confronted with different security risks. These risks range in danger and should always be dealt with accordingly. Unfortunately, not everyone is aware of the dangers or how to prevent them and this is where most of the issues arise in information technology (IT). When computer users do not take security into account many issues can arise from that like system compromises or loss of data and information. This is an obvious issue that is present with all computer users.
This book is intended to educate the average and experienced user of what kinds of different security practices and standards exist. It will also cover how to manage security software and updates in order to be as protected as possible from all of the threats that they face.
Conditions of Use
 This book is licensed under a Creative Commons License (CC BY). You can download the ebook The InfoSec Handbook for free.
- Title
- The InfoSec Handbook
- Subtitle
- An Introduction to Information Security
- Publisher
- Apress
- Author(s)
- Umesh Rao, Umesha Nayak
- Published
- 2014-08-30
- Edition
- 1
- Format
- eBook (pdf, epub, mobi)
- Pages
- 416
- Language
- English
- ISBN-10
- 1430263822
- ISBN-13
- 9781430263821
- License
- CC BY
- Book Homepage
- Free eBook, Errata, Code, Solutions, etc.
Title
Copyright
About ApressOpen
Dedication
Contents at a Glance
Contents
About the Authors
Acknowledgments
Introduction
Part I: Introduction
    Chapter 1: Introduction to Security
        What is Security?
        Why is Security Important?
        What if You Do Not Care About Security?
        The Evolution of the Computer and Information Security
        Information Security Today
        Applicable Standards and Certifications
        The Role of a Security Program
    Chapter 2: History of Computer Security
        Introduction
        Communication
        World Wars and Their Influence on the Field of Security
            Cypher Machine: Enigma
            Code Breakers
            Some Historical Figures of Importance: Hackers and Phreakers
            Kevin Mitnick
        Chapter Summary
Part II: Key Principles and Practices
    Chapter 3: Key Concepts and Principles
        Introduction
        Security Threats
            External and Internal Threats
            Information Security Frameworks and Information Security Architecture
        Pillars of Security
            People
            Policies, Procedures, and Processes
            Technology
        Information Security Concepts
            CIA Triad
            Parkerian Hexad
        Implementation of Information Security
            Risk Assessment
            Planning and Architecture
            Gap Analysis
            Integration and Deployment
            Operations
            Monitoring
            Legal Compliance and Audit
            Crisis Management
        Principles of Information Security
        Chapter Summary
    Chapter 4: Access Controls
        Introduction
            Confidentiality and Data Integrity
            Who Can Access the Data?
        What is an Access Control?
            Authentication and Authorization
            Authentication and Access Control Layers
            Access Control Strategies
        Implementing Access Controls
            Access Control Lists (ACLs)
            AAA Framework
            LDAP and Active Directory
            IDAM
        Chapter Summary
    Chapter 5: Information Systems Management
        Introduction
            Risk
            Incident
            Disaster
            Disaster Recovery
            Business Continuity
        Risk Management
            Identification of Risk
            Risk Analysis
            Risk Responses
            Execution of the Risk Treatment Plans
            The Importance of Conducting a Periodic Risk Assessment
        Incident Response
            Incident Response Policy, Plan, and Processes
            Incident Response Teams
            Ensuring Effectiveness of Incident Response
        Disaster Recovery and Business Continuity
            How to Approach Business Continuity Plan
        Chapter Summary
Part III: Application Security
    Chapter 6: Application and Web Security
        Introduction
        Software Applications
            Completeness of the Inputs
            Correctness of the Inputs
            Completeness of Processing
            Correctness of Processing
            Completeness of the Updates
            Correctness of the Updates
            Preservation of the Integrity of the Data in Storage
            Preservation of the Integrity of the Data while in Transmission
            Importance of an Effective Application Design and Development Life Cycle
            Important Guidelines for Secure Design and Development
        Web Browsers, Web Servers, and Web Applications
            Vulnerabilities in Web Browsers
            Vulnerabilities of Web Servers
            Web Applications
        Chapter Summary
    Chapter 7: Malicious Software and Anti-Virus Software
        Introduction
        Malware Software
            Introduction to Malware
        Types of Malware in Detail
            Spyware
            Adware
            Trojans
            Viruses
            Worms
            Backdoors
            Botnets
        A Closer Look at Spyware
            Trojans and Backdoors
            Rootkits
            Viruses and Worms
            Botnets
        Brief History of Viruses, Worms, and Trojans
            The Current Situation
        Anti-Virus Software
            Need for Anti-Virus Software
        Top 5 Commercially Available Anti-Virus Software
            Symantec Norton Anti-Virus Software
            McAfee Anti-Virus
            Kaspersky Anti-Virus
            Bitdefender Anti-Virus
            AVG Anti-Virus Software
        A Few Words of Caution
        Chapter Summary
    Chapter 8: Cryptography
        Introduction
        Cryptographic Algorithms
        Symmetric Key Cryptography
            Key Distribution
        Asymmetric Key Cryptography
            Public Key Cryptography
            RSA Algorithm
            Advantages of Public Key Cryptography
            Applications of PKC
            Public Key Infrastructure (PKI)
            Certificate Authority (CA)
            Digital Certificate
        Hash Function Cryptography
            Popular Hashes
            Digital Signatures
        Summary of Cryptography Standard Algorithms
        Disk / Drive Encryption
        Attacks on Cryptography
        Chapter Summary
Part IV: Network Security
    Chapter 9: Understanding Networks and Network Security
        Introduction
        Networking Fundamentals
        Computer Communication
        Network and its Components
            Network Protocols
        Network Vulnerabilities and Threats
            Vulnerabilities
            Threats
            Attacks
        Chapter Summary
    Chapter 10: Firewalls
        Introduction
            How Do You Protect a Network?
        Firewall
            Basic Functions of Firewall
            Packet Filtering
            Stateful Packet Filtering
            Network Address Translation (NAT)
            Application Level Gateways (Application Proxy)
        Firewall Deployment Architecture
            Option 1: Bastion Host
            Option 2: Staging Area or Demilitarized Zone (DMZ)
        Personal Firewall
            Firewall Best Practices
            Auditing of Firewall
        Chapter Summary
    Chapter 11: Intrusion Detection and Prevention Systems
        Introduction
        Why Use IDS?
            Types of IDS
        How Does Detection Work?
            Signature-Based Detection
            Anomaly-Based Detection
        IDS/IPS System Architecture and Framework
            Appliance (Sensors)
            Signature Update Server
            IDS/IPS in Context
        Chapter Summary
    Chapter 12: Virtual Private Networks
        Introduction
        Advantages of VPN
        VPN Types
            Remote Access (Host-to-Site) VPN
            Site-to-Site (Intranet and Extranet) VPN
        VPN and Firewall
        VPN Protocols
            Tunneling
            Data Authentication and Data Integrity
            Anti-Replay Services
            Data Encryption
            Layer Two Tunneling Protocol (L2TPv3)
            Generic Routing Encapsulation (GRE)
            Internet Protocol Security (IPSec)
        MPLS (Multi-Protocol Label Switching)
            MPLS VPN
            MPLS VPN Security
            Important IETF Standards and RFCs for VPN Implementation
        A Few Final Thoughts about VPN
        Chapter Summary
    Chapter 13: Data Backups and Cloud Computing
        Introduction
        Need for Data Backups
        Types of Backups
            Category 1: Based on current data on the system and the data on the backups
            Category 2: Based on what goes into the backup
            Category 3: Based on storage of backups
            Category 4: Based on the extent of the automation of the backups
            RAID Levels
            Other Important Fault Tolerance Mechanisms
            Role of Storage Area Networks (SAN) in providing Backups and Disaster Recovery
            Cloud Infrastructure in Backup Strategy
            Database Backups
        Backup Strategy
            Restoration Strategy
            Important Security Considerations
            Some Inherent Issues with Backups and Restoration
            Best Practices Related to Backups and Restoration
        Introduction to Cloud Computing
            What is Cloud Computing?
        Fundamentals of Cloud Computing
            Cloud Service Models
        Important Benefits of Cloud Computing
            Upfront Capital Expenditure (CAPEX) versus Pay as you use Operational Expenditure (OPEX)
            Elasticity or Flexibility
            Reduced need for specialized resources and maintenance services
            On-Demand Self-Service Mode versus Well-Planned Time-Consuming Ramp Up
            Redundancy and Resilience versus Single Points of Failure
            Cost of traditional DRP and BCP versus the DRP & BCP through Cloud Environment
            Ease of use on the Cloud Environment
        Important Enablers of Cloud Computing
        Four Cloud Deployment Models
            Private Cloud
            Public Cloud
            Community Cloud
            Hybrid Cloud
        Main Security and Privacy Concerns of Cloud Computing
            Compliance
            Lack of Segregation of Duties
            Complexity of the Cloud Computing System
            Shared Multi-tenant Environment
            Internet and Internet Facing Applications
            Control of the Cloud Consumer on the Cloud Environment
            Types of Agreements related to Service Levels and Privacy with the Cloud Provider
            Data Management and Data Protection
            Insider Threats
            Security Issues on account of multiple levels
            Physical security issues related to Cloud Computing environment
            Cloud Applications Security
            Threats on account of Virtual Environment
            Encryption and Key Management
        Some Mechanisms to address the Security and Privacy Concerns in Cloud Computing Environment
            Understand the Cloud Computing environment and protect yourself
            Understand the Technical Competence and segregation of duties of the Cloud Provider
            Protection against Technical Vulnerabilities and Malicious Attacks
            Regular Hardening and Appropriate Configurations of the Cloud Computing Environment
            Data Protection
            Encryption
            Good Governance Mechanisms
            Compliance
            Logging and Auditing
            Patching / Updating
            Application Design and Development
            Physical Security
            Strong Access Controls
            Backups
            Third-Party Certifications / Auditing
        Chapter Summary
Part V: Physical Security
    Chapter 14: Physical Security and Biometrics
        Introduction
        Physical and Technical Controls
            ID Cards and Badges
            Photo ID cards
            Magnetic Access Cards
            Other Access Mechanisms
            Locks and Keys
            Electronic Monitoring and Surveillance Cameras
            Alarms and Alarm Systems
        Biometrics
            Some of the important biometric mechanisms
            How the biometric system works
            Enrollment
            Recognition
            Performance of the Biometrics System
            The test of a good biometric system
            Possible information security issues with the Biometric Systems
            Multimodal biometric system
            Advantages of Biometric systems
        Administrative Controls
            Fire Safety Factors
            Interception of Data
            Mobile and Portable Devices
            Visitor Control
        Chapter Summary
    Chapter 15: Social Engineering
        Introduction
        Social Engineering Attacks: How They Exploit Human Nature
            Helping Nature
            Trusting Nature
            Obeying the Authority
            Fear
        Social Engineering: Attacks Caused by Human Beings
        Social Engineering: Attacks Caused by Computers or Other Automated Means
        Social Engineering: Methods that are Used for Attacks
        Social Engineering: Other Important Attack Methods
        Social Engineering: How to Reduce the Possibility of Falling Prey to Attacks
        Chapter Summary
    Chapter 16: Current Trends in Information Security
        Wireless Security
            Bluetooth Technology and Security
        Mobile Security
        Chapter Summary
    Bibliography
        Chapter 1
            Footnotes
            References
        Chapter 2
            Footnotes
            Additional References
        Chapter 3
            Footnotes
        Chapter 4
            Footnotes
        Chapter 5
            Footnotes
        Chapter 6
            Footnotes
            Additional References
        Chapter 7
            Footnotes
        Chapter 8
            Footnotes
            Additional References
        Chapter 9
            Footnotes
            Additional References
        Chapter 10
            Footnotes
            Additional References
        Chapter 11
            Footnotes
            Additional References
        Chapter 12
            Footnotes
            Additional References
        Chapter 13
            Footnotes
            References
        Chapter 14
            Footnotes
            References
            Additional References
        Chapter 15
            Footnotes
            Additional References
        Chapter 16
            Footnotes
Index